Policy
Central policy controls
Set the boundaries for applications, data, and connected actions in one place.
View featureAgent Platform · Governance
กำกับ AI Agent โมเดล ข้อมูล และแอปด้วย inventory นโยบาย การอนุมัติ หลักฐานต่อเนื่อง observability และการตัดสินใจที่ตรวจสอบได้
Bring access, application policy, approval, and audit evidence into one governed operating view.
Explore all featuresSet the boundaries for applications, data, and connected actions in one place.
View featureGive owners a clear view of who has access and what needs review.
View featureTrack which products are connected and how they inherit organizational rules.
View featureRoute sensitive changes to the right person before they take effect.
View featureKeep decisions, policy changes, and access events available for review.
View featureMake permitted access and protected actions understandable across teams.
View featureAI + AGENT GOVERNANCE CONTROL PLANE
Outborn Governance connects agents, models, data, applications, policy, infrastructure and decision evidence so governance stays continuous and close to execution—not in a spreadsheet reconstructed after the work is done.
01 / REQUEST
03 / OUTCOME
FROM DISCOVERY TO EVIDENCE
Context and policy travel with a resource from discovery through decision and into durable evidence, so teams do not have to reconstruct the story later.
Data, knowledge, AI, applications and infrastructure enter one governed graph with stable identity and business context.
Ownership, lineage, quality, classification, privacy, environment, posture and AI risk are evaluated together.
A consequential action can be allowed, denied, sent for approval or held for review before it crosses a governed boundary.
The outcome, policy decision and supporting context remain available to operators, governance teams and auditors.
CONTINUOUS AI GOVERNANCE
Discover
Inventory governed data, knowledge, AI and infrastructure with ownership, classification, lineage and lifecycle context.
Understand
Connect technical lineage to business meaning, responsible people, policies, decisions, evidence and outcomes.
Govern
Evaluate access, privacy, residency, AI risk and consequential actions before work crosses a governed boundary.
Observe
Track quality, SLOs, infrastructure posture, change, missing resources and durable governance events over time.
Control AI
Govern model and agent inventory, risk, evaluations, data access, human oversight and action boundaries.
Prove
Preserve policy decisions, reviews, exceptions, control tests and the record that explains what happened and why.
CLEAR TRUST BOUNDARIES
Governance becomes safer and easier to reason about when identity, policy state, provider credentials and provider execution do not collapse into one service.
Human identity, membership and tenant selection stay with the shared identity layer.
Governance owns policy state, topology, observations, decisions, evidence and audit.
Provider credentials and provider-side execution remain in the connection layer instead of being copied into Governance.
DESIGNED FOR AI, AGENTS, DATA + INFRASTRUCTURE
Maintain model and agent inventory, ownership, risk, evaluations, data access, human oversight and action boundaries.
Catalog, glossary, lineage, ownership, certification, quality and data-product context.
Classification, purpose, retention, access decisions, periodic review and auditable reasoning.
Environments, resource graphs, drift, posture evidence, SLOs, resilience and residency.
Controls, tests, exceptions, evidence and audit readiness without a second source of truth.
Goals, projects, outcomes, assumptions and source-backed evidence around important decisions.
OUTBORN GOVERNANCE
Start with the governance problem that creates the most operational friction, then connect the controls that need to stay true as the organization changes.
HUMAN APPROVAL IN THE LOOP
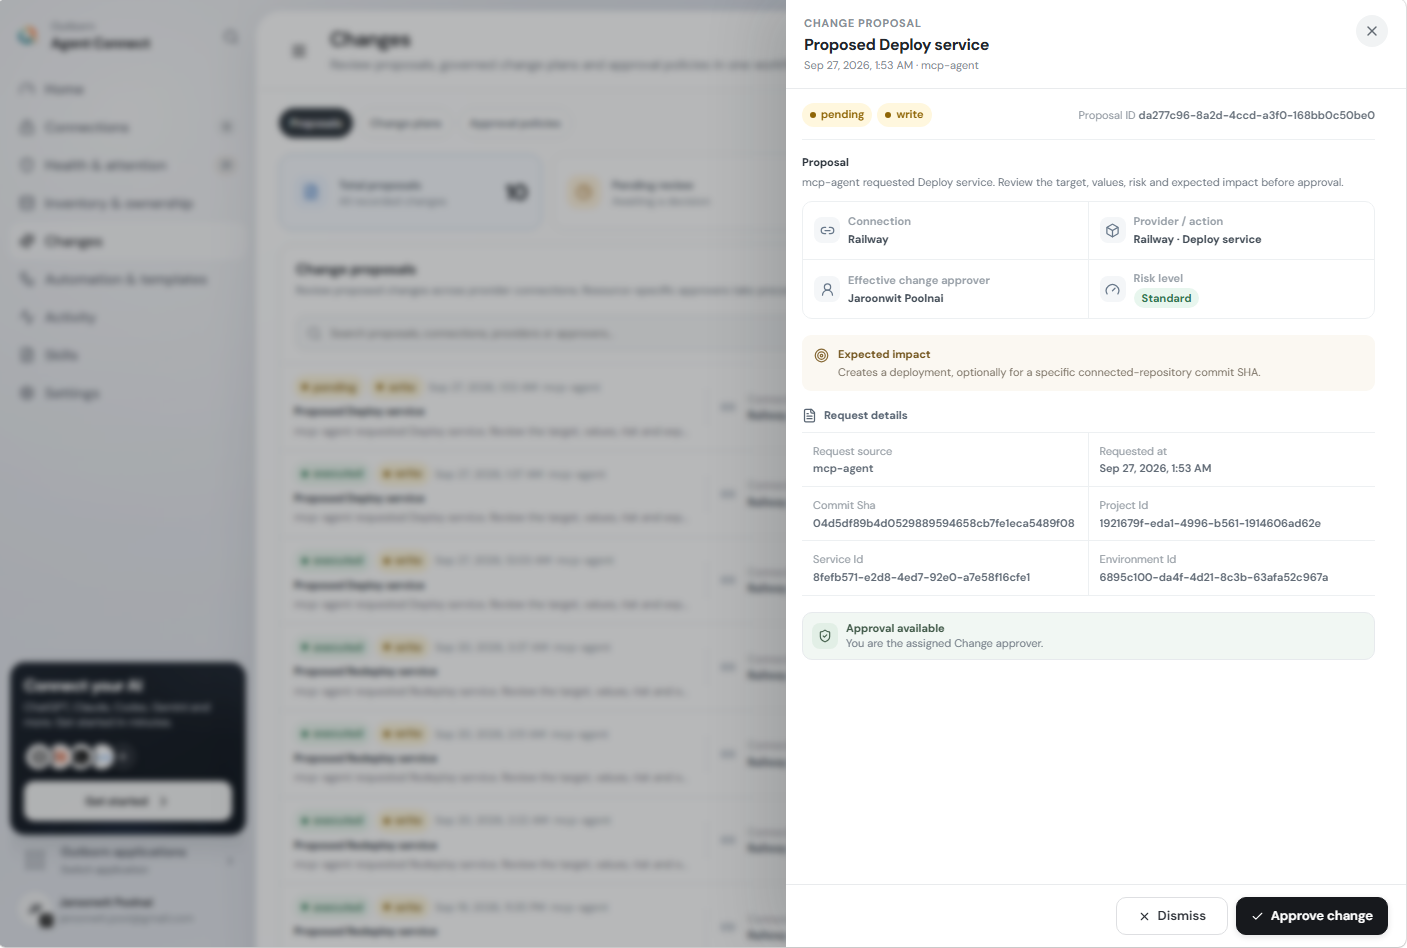
Connected actions stay reviewable. When a deployment needs approval, the request goes to the team’s Agent Connect approval flow before it can run.
Deploy the service to production now.
Your approval here is noted, but the Outborn Agent Connect connector still requires the proposal to be approved inside its own approval UI before the deployment can execute.
Use proposal 0c4af2c3-7ad9-4dfd-8125-cc25cb6d8a5b in Outborn Agent Connect → Approvals / Pending proposals, approve “Proposed Deploy service”, then tell me approved there and I’ll continue the DB/state migration immediately.
Review connected actions in their source application before execution.
IN AGENT CONNECT
Open the pending change in Agent Connect to review its scope, impact and approval status.