01 / IDENTITY
One account, every product.
Start with your identity and sign in securely to the Outborn ecosystem.
◉Outborn AccountIllustrative interface · sample data
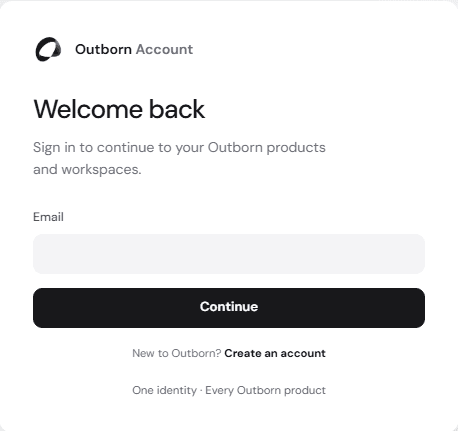
 Outborn AccountONE ACCOUNT FOR EVERY PRODUCT
Discover the account experience behind secure sign-in, organization membership and approved application access.
Start with your identity and sign in securely to the Outborn ecosystem.
Keep organizations distinct while staying signed in as the same person.
Add MFA and passkeys before accessing protected organizational resources.
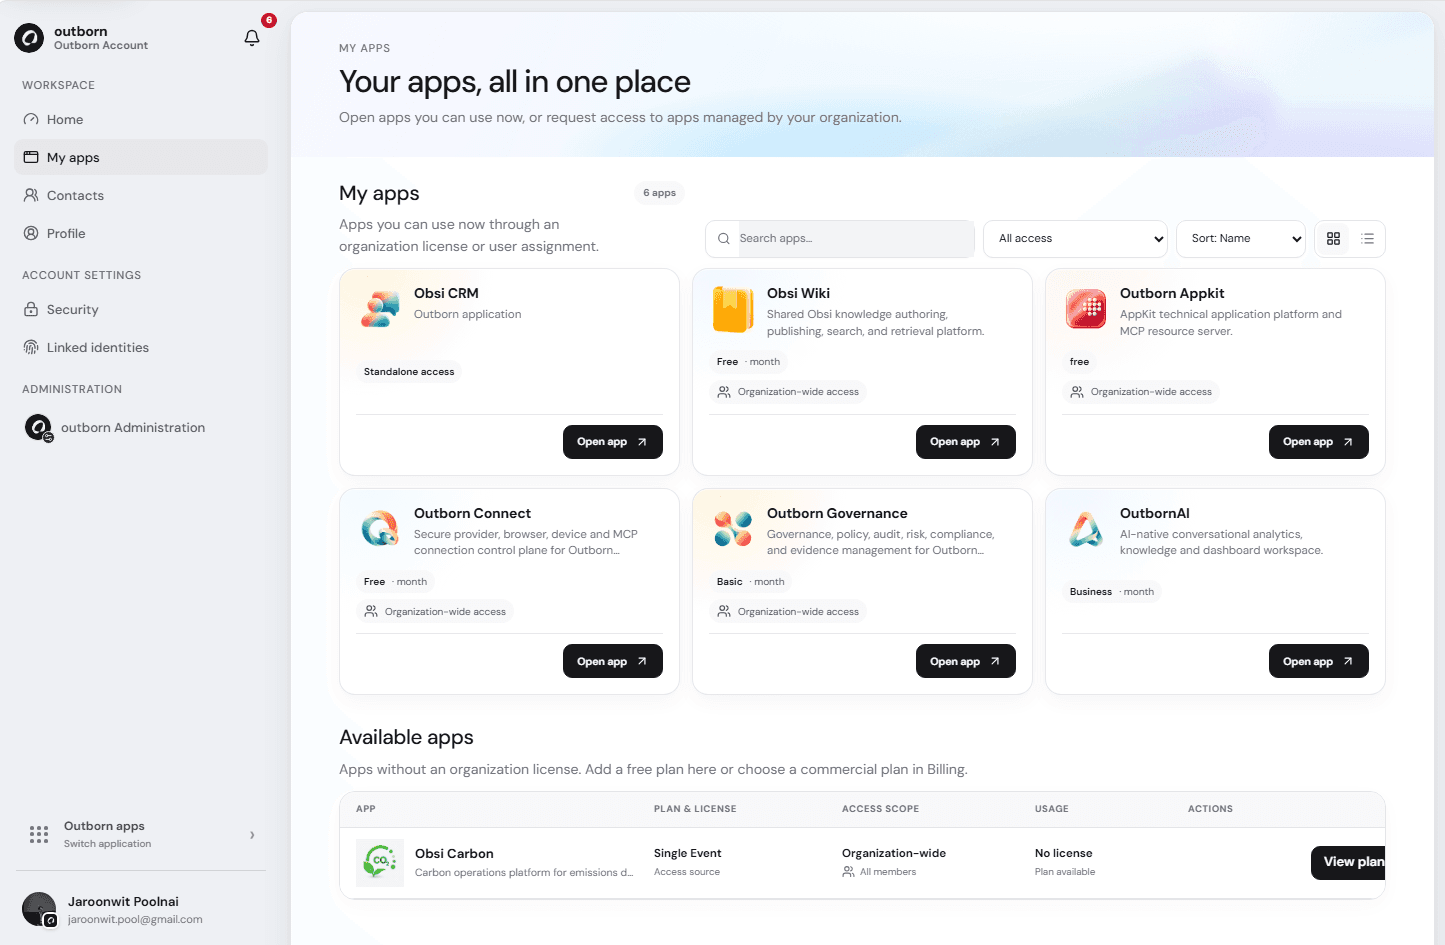
See available applications and continue into the products your organization can use.
HOW ACCOUNT WORKS
ID、安全な認証、アクセスできる組織をひとつの入口にまとめます。
Use one account
Conceptual flow · Each organization and product retains its own permission controls.
ID → セキュリティ → 組織 → 承認済みアプリ。Account がその流れをつなぎます。
できること / Outborn Account
Identity, security, organizations and approved apps stay connected at every step.
Use one account
Centralize access
Strengthen security
すべての Outborn 製品で使える、安全な共通IDとアクセス基盤。
もたらす価値
Less friction between sign-in, permissions, and getting to work.
WHAT OUTBORN ACCOUNT IS FOR
Outborn Account is the shared entry point for identity and access. It keeps one person, their secure sign-in, their organization memberships, and their available applications connected instead of recreating those pieces inside every product.
The goal is simple: a person should understand who they are signed in as, which organization they are working in, and which applications they can enter before they start working with product-specific data and permissions.
HOW IT WORKS
Account establishes the shared identity first; organizations and applications then decide where that identity is allowed to work.
Use one Outborn identity as the starting point for the products and organizations you belong to.
Strengthen sign-in with multi-factor authentication and passkeys instead of creating separate security setups in every app.
Your account keeps organization memberships attached to the same identity, so work stays separated by the organization you are acting in.
See the Outborn and Obsi applications available to you and continue into the products your organization has made accessible.
When memberships or application access change, the shared identity remains the stable place from which those changes take effect.
CORE CAPABILITIES
A consistent account follows the person across the Outborn ecosystem instead of asking every product to create another identity silo.
Keep the organizations you work with connected to the same account while preserving which organization you are currently working inside.
Add stronger authentication at the account layer so secure sign-in is shared across connected product journeys.
Bring available Outborn and Obsi applications into one place and make the route into each approved product easier to understand.
Identity is shared, but access is not assumed. Organization membership and product availability still determine where a person can go.
Move between connected products without losing the identity and organization context that explains who you are acting as.
WHERE ACCOUNT STOPS
Account carries identity and access context across the ecosystem, but organization administration and each product still own their own authorization decisions. That separation keeps one account convenient without flattening every permission boundary.
Who you are, how you sign in, which organizations you belong to, and which connected applications are available to you.
Who should have access, which applications are enabled, and how organization-level permissions are administered.
What you can do after entering the application, based on that product’s own roles, data, and workflow permissions.
CONNECTED ECOSYSTEM
Your shared identity connects to the Outborn products and organizational context you can access.
OUTBORN ACCOUNT
Start with one account. Stay connected to the organizations and products that matter.